SSL Certificates Explained: How HTTPS Protects Your Website
SSL certificates are a basic requirement for almost every modern website. They enable HTTPS, protect information exchanged between visitors and the web server, and help browsers confirm that a connection is being made to the intended domain. Whether you run a personal blog, an online shop or a business portal, choosing and maintaining the right certificate is an essential part of website security.
What an SSL Certificate Actually Protects
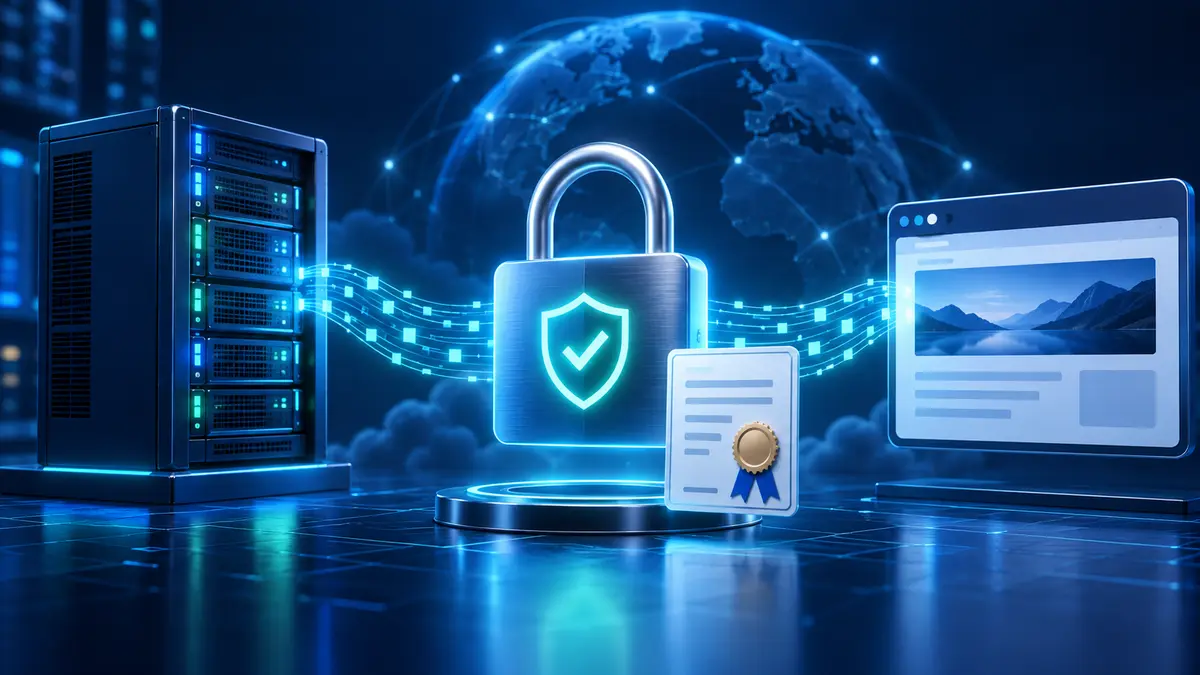
When a browser connects to a website over HTTPS, the server presents its certificate and proves that it controls the associated private key. The browser checks whether the certificate is valid, trusted and issued for the requested hostname. The two sides then establish an encrypted connection using TLS.
This encryption prevents someone observing the network from easily reading passwords, contact forms, payment details or other information in transit. It also protects data integrity by making undetected modification much more difficult. The ClouDNS overview of SSL certificates offers a useful introduction to the certificate and handshake process.
Choose the Appropriate Validation Level
Domain Validation (DV) certificates confirm control of a domain and are suitable for blogs, portfolio sites and many small business websites. They are usually issued quickly and provide the same connection encryption as more expensive certificate types.
Organization Validation (OV) certificates also verify information about the organization requesting the certificate. Extended Validation (EV) applies a more detailed verification process. OV or EV may be appropriate when verified business identity is important, but visitors should still evaluate the website itself rather than relying on a certificate alone.
Match the Certificate to Your Hostnames
A standard single-domain certificate may cover one hostname or a defined combination such as the root domain and its www version. A wildcard certificate can protect multiple first-level subdomains, while a multi-domain certificate can include several different hostnames.
List every hostname that must work over HTTPS before ordering or issuing the certificate. Understanding how DNS connects a domain name to hosting also helps prevent validation and installation mistakes.
Plan Installation and DNS Validation Carefully
The certificate and its intermediate chain must be installed on every web server, proxy or load balancer that terminates HTTPS. The private key should remain protected and must never be published or transferred through insecure channels.
Many automated certificate authorities support DNS-based validation. This requires adding a temporary TXT record to prove control of the domain. If validation is delayed, check that the record is published on the authoritative nameservers and consider how DNS TTL affects cached records.
Automate Renewal and Monitor Expiration
Certificates have limited validity periods and must be renewed or reissued before they expire. An expired certificate produces a prominent browser warning and can make a website effectively unavailable to visitors.
Use an automated renewal client whenever your hosting environment supports it. Renewal automation should include a post-renewal reload of the web server and regular tests from outside the server. Monitoring the certificate expiration date provides an additional safety net if automation fails.
Finally, test the complete HTTPS configuration after installation: confirm redirects from HTTP, look for mixed-content resources and verify every public hostname. A certificate is only one part of a secure deployment, but careful selection, installation and renewal make it a dependable foundation.